Key Takeaways
- Relying purely on expensive firewalls guarantees a catastrophic breach; you need a structured operational defence to survive modern threats.
- The updated 2.0 release shifts focus to high-level corporate governance, forcing board members to take direct responsibility for cyber risks.
- Treating artificial intelligence like basic software is a massive error; you must deploy rigid algorithmic guardrails to stop automated data leaks.
Throwing cash at random antivirus software does not protect a corporate network. When a vicious ransomware gang locks down your digital infrastructure, chaotic reactions guarantee total bankruptcy. You must execute a ruthless, organised defence strategy before the attack happens. The NIST Cybersecurity Framework is the gold standard for digital survival. It is a brutal, tactical blueprint that forces your IT department to identify vulnerabilities, lock down assets, and strike back during a massive breach. Stop operating completely blind. Master the core functions, enforce corporate governance, and build an indestructible perimeter that permanently shuts down hackers before they steal your critical data.
What is the NIST Cybersecurity Framework?
NIST is a mandatory set of strict guidelines, heavy standards, and tactical best practices engineered by the federal government to protect critical infrastructure. It completely removes the guesswork from securing a network. Instead of letting low-level IT guys randomly buy security tools, this structure dictates exactly how a corporation must prepare for, survive, and recover from a brutal digital attack. It forces businesses to view data protection as a massive financial risk, not just a technical annoyance.
Understanding the Core Functions of the NIST Cybersecurity Framework
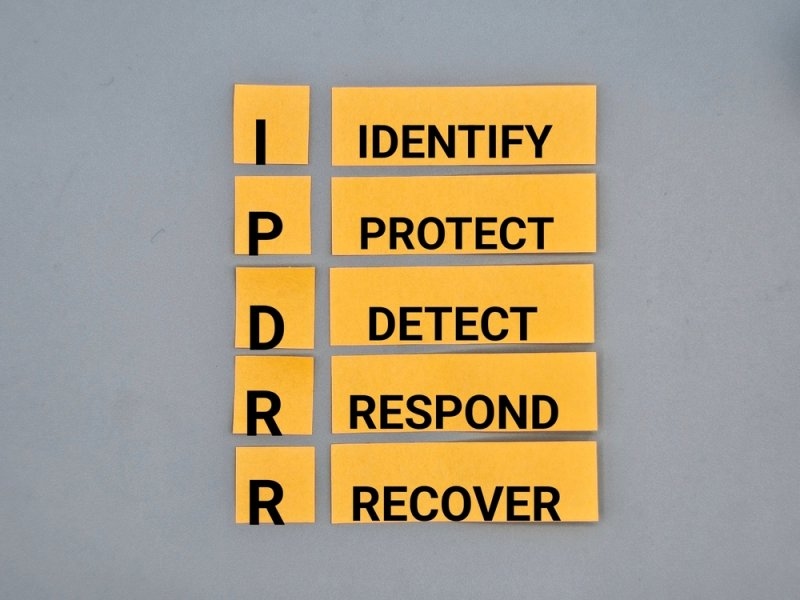
Stop improvising when hackers breach the firewall. You must execute these exact six functions to build a completely indestructible digital fortress.
Govern
This new addition forces upper management to establish strict internal policies and take brutal financial accountability for their digital supply chain risks.
Identify
You cannot protect hardware you do not know exists. Map every single laptop, server, and piece of software touching the network so there are zero blind spots.
Protect
This is the heavy armour. It demands enforcing brutal access controls, executing mandatory employee security training, and heavily encrypting all sensitive data.
Detect
Hackers will eventually breach the perimeter. Deploy aggressive network monitoring tools to instantly spot unusual data movements and hunt down malicious code operating silently.
Respond
The second your system throws a red flag, freaking out just ruins the digital crime scene. Yank the infected machines completely off the network to trap the code, and get the cops involved before the damage spreads.
Recover
Wipe infected drives, restore clean offline backups, and immediately rebuild the shattered network infrastructure to resume normal business operations.
Executing a Flawless NIST Framework Implementation
A proper NIST Framework implementation requires brutal organisational discipline. You cannot just read the manual; you must execute these precise technical strikes to lock down the perimeter.
Audit the Stack
Deploy NIST CSF compliance software to tear down outdated legacy systems and expose every single hidden vulnerability across the existing hardware infrastructure.
Strip the Privileges
Rip away administrator access from standard employees instantly, guaranteeing that a single compromised email account cannot hijack the entire core network.
Interrogate the Vendors
Third-party software suppliers to legally prove their code is entirely secure before connecting their tools to your data.
Run the drills.
Ruthlessly test incident response protocols by actively shutting down the network during mock ransomware attacks to expose operational failures.
What are the benefits of the NIST CSF 2.0 Framework?
You are not just filling out federal compliance checklists. Deploying this exact architecture completely revolutionises how your business survives a catastrophic hack.
Executive Accountability
It permanently stops board members from blaming the IT guys. The new governance rules force leadership to actively manage digital risks.
Universal Communication
It destroys technical jargon. The framework gives executives and engineers a shared language so the CEO actually understands the severe financial threat of a breached server.
Supply Chain Lockdown
Hackers breach your weakest software vendor. This structure forces you to audit third-party suppliers before they infect your network.
Reduced Legal Fines
Proving you rigorously followed federal security standards drastically lowers the brutal regulatory fines issued by government agencies after an inevitable breach.
Also Read: NIST Compliance Checklist: Essential Steps for Businesses
Why Did the Government Release the NIST Cybersecurity Framework 2.0?
Cyber warfare changed over the last decade. Looking at the NIST Cybersecurity Framework 2.0 update, you see a massive shift away from just protecting heavy physical infrastructure.
Universal Targeting
The government realised that small schools and basic e-commerce sites were getting completely wiped out by ransomware, requiring a scalable defence model.
Jargon Elimination
The 2.0 version strips away the dense critical-infrastructure language, making the tactical rules accessible to absolutely any business operating online.
Leadership Accountability
It weaponises the new governance function, proving that a digital breach is no longer just a technical failure but a massive corporate leadership disaster.
Why AttestPath?
Manually tracking federal security standards guarantees vulnerabilities. AttestPath.ai destroys this operational nightmare. As an agent-powered compliance platform, it ruthlessly automates your entire digital defence. It instantly maps your infrastructure to frameworks like NIST, SOC 2, and ISO 27001, bulletproofing the network to secure certifications effortlessly.
Conclusion
Stop leaving the corporate vault completely unlocked while hoping hackers ignore you. Relying on outdated antivirus subscriptions guarantees your entire company will be held for crypto ransom. Building an indestructible digital perimeter requires massive discipline and a ruthless operational blueprint. Implementing the NIST Cybersecurity Framework forces your entire organisation to treat digital threats like active physical warfare. Stop ignoring the vulnerabilities buried in your software supply chain.
Frequently Asked Questions
How does mapping this framework to ISO 27001 actually work?
These two massive security structures stack perfectly. While the American federal guidelines provide a flexible, tactical approach to identifying threats, ISO 27001 requires strict formal auditing to achieve an actual global certification. Organisations aggressively cross-reference them to build an impenetrable defence that passes brutal international compliance checks.
Can a small business survive the costs of deploying this exact architecture?
Absolutely. The entire system is highly scalable. A massive international bank will spend millions locking down complex server clusters, but a local dental office can use the same tactical blueprint to simply secure their Wi-Fi, enforce strong passwords, and back up patient files without spending a massive fortune.
Does following these federal guidelines stop all ransomware infections?
No security system is entirely bulletproof. If a lazy employee blindly downloads a toxic email attachment, the malicious script will execute. The architecture drastically minimises the blast radius, ensuring you instantly detect the rogue encryption and shut down the infected machine before it destroys the entire network.
How often should a company audit their digital defence profile?
Executing a heavy technical audit once a year is a massive tactical failure. Corporations must continuously monitor network traffic and run penetration tests quarterly. Any time the company buys new software or migrates data to a new cloud server, the entire risk profile must be brutally re-evaluated immediately.
Why does the government care so much about third-party vendor risks?
Hackers actively hunt for tiny, unsecured software plugins that major corporations use. If a hacker breaches a basic payroll app, they instantly gain a backdoor into thousands of corporate networks simultaneously. This is exactly why modern security mandates demand you interrogate all external vendors.




